CyberSafe LogoCyberSafe

Services

Thirty-three practices.
One continuous security operation.

Every CyberSafe engagement starts with understanding your environment. What follows is scoped from the practices below — not sold as a bundle you don't need.

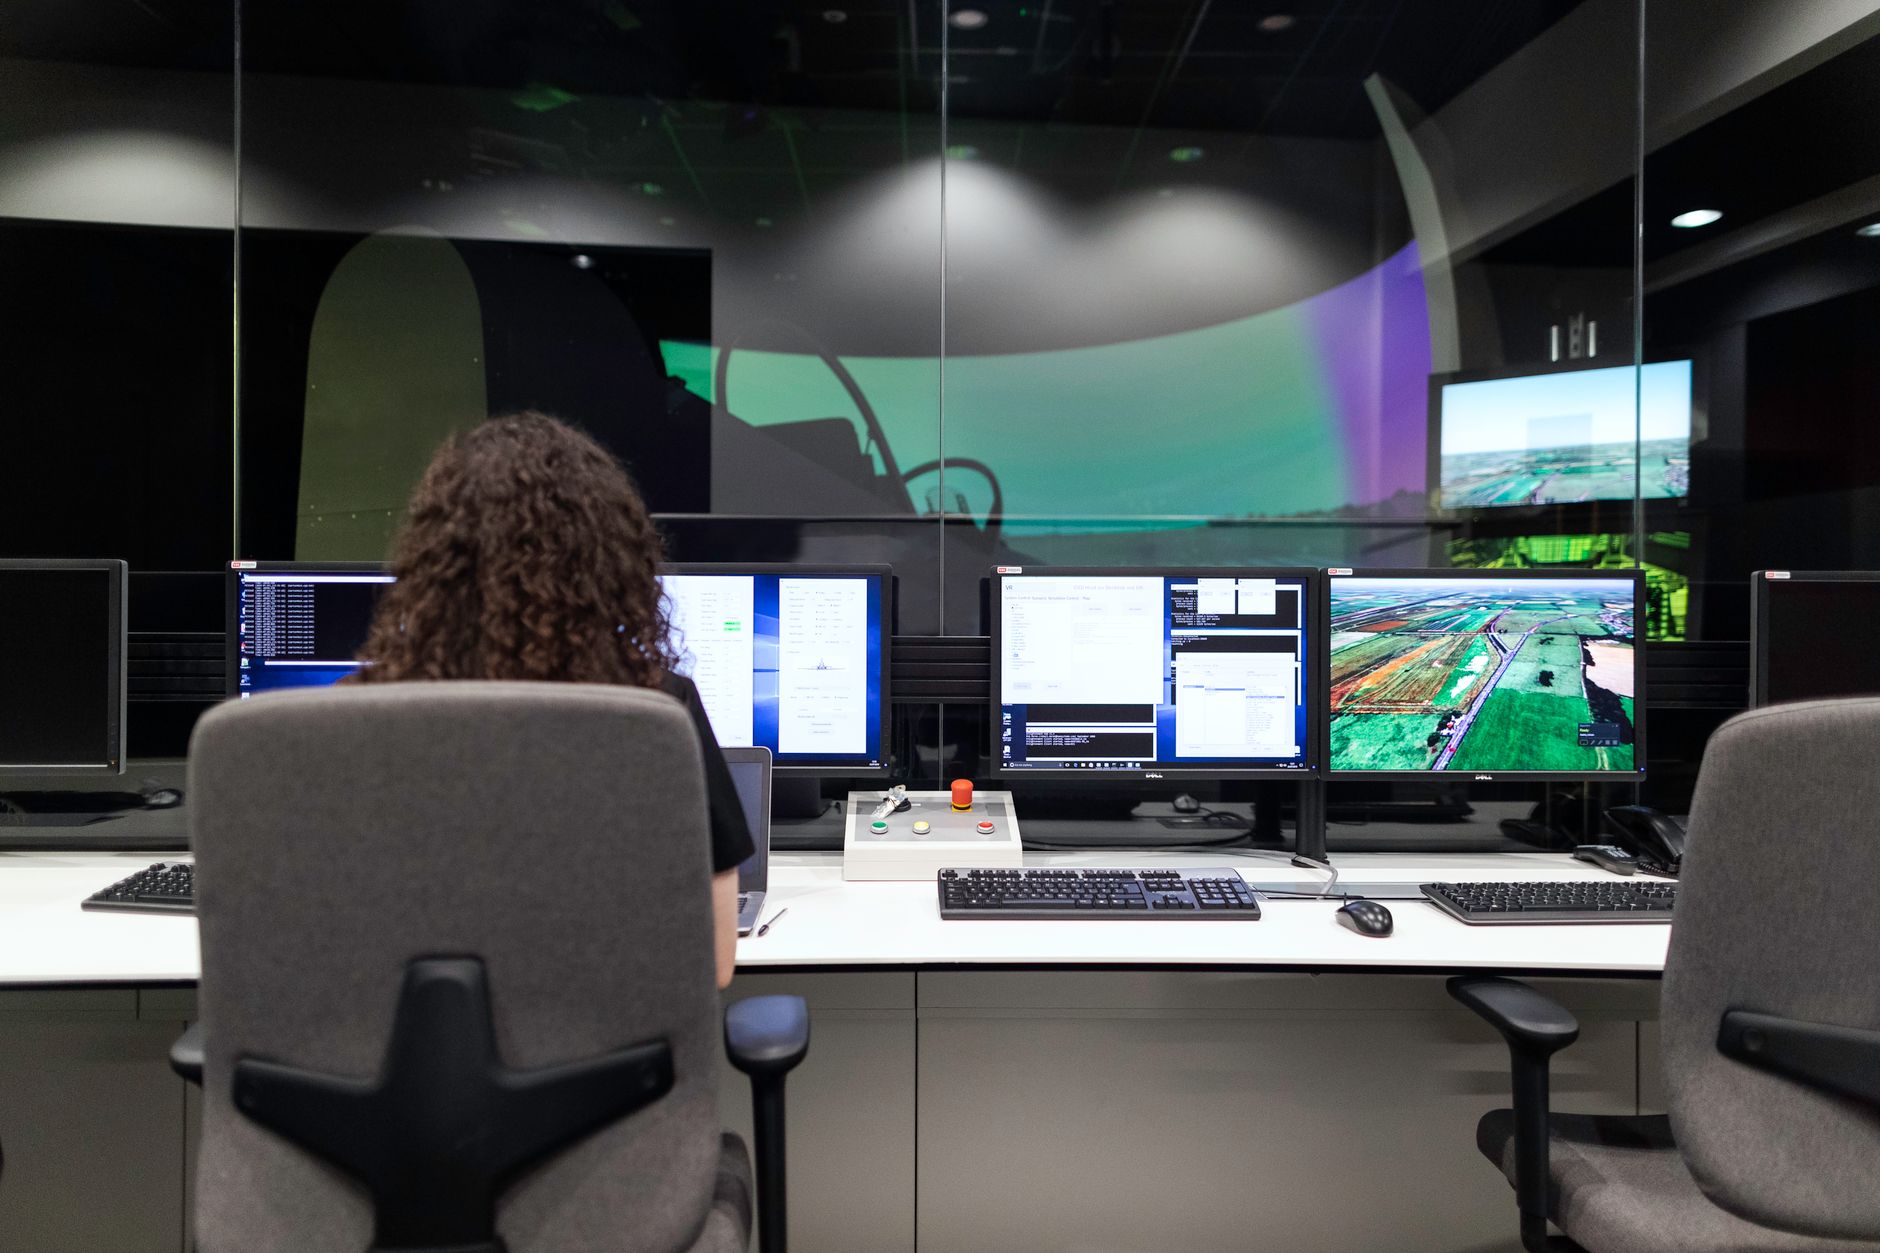
Cybersecurity assessment mapping real exposure
01

Cybersecurity Assessments

Establish an accurate, evidence-based picture of your current exposure.

  • Security posture assessments
  • Cyber risk assessments
  • Vulnerability assessments
  • Security audits
  • Security gap analysis
Penetration testing keyboard and exploit lab
02

Penetration Testing

Prove what an attacker could actually do inside your environment.

  • Network penetration testing
  • Web application penetration testing
  • API penetration testing
  • Infrastructure testing
  • Vulnerability validation
  • Security testing
Vulnerability management across monitoring screens
03

Vulnerability Management

Turn a scan backlog into a prioritised, closeable remediation plan.

  • Vulnerability scanning
  • Vulnerability identification
  • Risk prioritization
  • Remediation guidance
  • Continuous vulnerability monitoring
Wall of security monitoring screens
04

Security Monitoring

Continuous visibility so an intrusion doesn't stay quiet for months.

  • Security event monitoring
  • Threat detection
  • Alert monitoring
  • Log analysis
  • Suspicious activity detection
  • Incident investigation
Managed security coverage in a data centre
05

Managed Cybersecurity

Security operations run for you, without building an internal SOC.

  • Managed security services
  • Continuous security monitoring
  • Endpoint protection management
  • Security infrastructure management
  • Security operations support
Incident response on a darkened operations laptop
06

Incident Response

Contain fast, understand precisely, recover with evidence intact.

  • Incident investigation
  • Threat containment
  • Malware investigation
  • Breach response
  • Recovery support
  • Post-incident analysis
Digital forensics analysis workstation
07

Digital Forensics

Reconstruct what happened, in a form that stands up to scrutiny.

  • Digital evidence analysis
  • Incident forensics
  • Endpoint investigation
  • Data recovery
  • Attack reconstruction
Security awareness classroom
08

Security Awareness & Training

Reduce the human attack surface with practice, not lectures.

  • Employee cybersecurity training
  • Phishing awareness
  • Social engineering awareness
  • Security best practices
  • Security culture programs
  • Phishing simulations
Cyber risk heatmap and analytics
09

Risk Management

Translate technical findings into decisions leadership can act on.

  • Cyber risk identification
  • Risk assessments
  • Risk prioritization
  • Risk mitigation strategies
  • Business continuity planning
  • Cyber resilience planning
GRC paperwork mapped to live controls
10

Governance, Risk & Compliance

The structure that keeps security consistent after the project ends.

  • Security policies
  • Security procedures
  • Governance frameworks
  • Compliance readiness
  • Control assessments
  • Risk registers
Abstract cloud infrastructure under review
11

Cloud Security

Find the misconfigurations that cause most cloud incidents.

  • Cloud security assessments
  • Cloud configuration reviews
  • Cloud vulnerability assessments
  • Identity & access security
  • Cloud security monitoring
Network cabling and racks attackers have to cross
12

Network Security

Design and verify the boundaries attackers have to cross.

  • Network security assessments
  • Firewall reviews
  • Network architecture reviews
  • Network segmentation
  • Secure network design
Endpoint laptop hardened against intrusion
13

Endpoint Security

Harden and watch the devices where most compromises begin.

  • Endpoint security assessments
  • Device protection
  • Endpoint monitoring
  • Endpoint hardening
  • Endpoint security management
Digital identity and access verification
14

Identity & Access Management

Control who can reach what — and prove it.

  • Identity security assessments
  • Access control reviews
  • Privileged access management
  • Multi-factor authentication strategy
  • Identity risk management
Application security code review
15

Application Security

Catch flaws in the code and APIs your business runs on.

  • Application security assessments
  • Secure development reviews
  • Web application security
  • API security
  • Application vulnerability testing
Encrypted data and database protection
16

Data Security

Know where sensitive data lives and who can move it.

  • Data security assessments
  • Data protection strategies
  • Sensitive data identification
  • Data access controls
  • Data loss prevention strategies
Security architecture design session
17

Security Architecture & Consulting

A security design that fits the business you actually run.

  • Cybersecurity strategy
  • Security architecture
  • Security roadmaps
  • Technology security consulting
  • Cybersecurity program development
Resilient server recovery environment
18

Business Continuity & Cyber Resilience

Plan for the incident that gets through, because one will.

  • Business continuity assessments
  • Disaster recovery planning
  • Cyber resilience assessments
  • Recovery planning
  • Incident preparedness
Security policy documentation
19

Security Policy & Documentation

Written control that survives staff turnover and audits.

  • Information security policies
  • Acceptable-use policies
  • Incident response policies
  • Access-control policies
  • Security procedures
  • Security documentation
Cybersecurity strategy planning
20

Cybersecurity Strategy

Where you are, where you need to be, and the order to get there.

  • Cybersecurity maturity assessments
  • Security roadmaps
  • Cybersecurity transformation
  • Security program design
  • Long-term security planning
Global threat intelligence on a digital globe
21

Threat Intelligence

Know what attackers are planning before they strike.

  • Personal threat intelligence
  • Advanced threat intelligence
  • Enterprise threat intelligence
  • Global threat intelligence
  • Threat landscape analysis
Dark-web monitoring research workstation
22

Dark Web Monitoring

Detect when your data or credentials appear on the dark web.

  • Dark web monitoring
  • Dark web & data leak monitoring
  • Credential breach detection
  • Data exposure alerts
  • Underground threat tracking
Artificial intelligence applied to threat detection
23

AI-Powered Security

Leverage artificial intelligence for advanced threat detection.

  • AI security assistant
  • Basic predictive analytics
  • Advanced AI detection
  • AI red team simulator
  • Machine learning threat analysis
XDR detection across correlated screens
24

Extended Detection & Response (XDR)

Unified security across endpoints, networks, and cloud.

  • Extended detection & response (XDR)
  • Advanced XDR
  • Cross-layer threat correlation
  • Automated response orchestration
  • Integrated security analytics
Zero Trust access verification
25

Zero Trust Security

Never trust, always verify. Secure access for modern environments.

  • Zero trust access
  • Zero trust architecture
  • Identity verification
  • Continuous authentication
  • Micro-segmentation
API security review at a developer workstation
26

API Security

Protect the APIs that connect your digital ecosystem.

  • API security scanner
  • API security & firewall
  • API penetration testing
  • API vulnerability assessment
  • API threat protection
Cloud security posture dashboard
27

Cloud Security Posture Management

Continuous monitoring and remediation of cloud misconfigurations.

  • Cloud security posture management (CSPM)
  • Cloud configuration monitoring
  • Compliance automation
  • Cloud risk assessment
  • Multi-cloud security management
Behavioral analytics graphs for insider and account risk
28

Behavioral Analytics

Detect threats by identifying anomalous user and system behavior.

  • Behavioral analytics
  • User behavior analytics (UBA)
  • Insider threat detection
  • Anomaly detection
  • Risk scoring
Attack-surface map of internet-facing assets
29

Attack Surface Monitoring

Continuous visibility into your external attack surface.

  • Attack surface monitoring
  • External exposure assessment
  • Digital footprint analysis
  • Asset discovery
  • Vulnerability prioritization
Data-loss prevention on a secured laptop
30

Data Loss Prevention

Prevent sensitive data from leaving your organization.

  • Data loss prevention (DLP)
  • Data classification
  • Sensitive data protection
  • Data exfiltration prevention
  • Compliance monitoring
SIEM log analysis across operations screens
31

SIEM Integration

Integrate security information for comprehensive visibility.

  • SIEM integrations
  • Log aggregation
  • Security event correlation
  • Custom alert rules
  • Threat hunting capabilities
Executive cybersecurity advisory briefing
32

vCISO & Advisory

Strategic cybersecurity leadership without the full-time cost.

  • vCISO / cybersecurity advisory
  • Virtual CISO services
  • Security program governance
  • Executive security guidance
  • Board-level reporting

Threat landscape

Every practice maps back to a live surface.

Assessments, testing, monitoring, and response are not separate catalogues. They are how CyberSafe keeps a current picture of cloud, identity, endpoints, and data — then closes the gaps that actually convert into incidents.

  • Internet-facing services, identity paths, and cloud defaults mapped as one surface
  • Automated probing tropes — phishing, credential stuffing, unpatched CVEs — ranked by impact
  • A continuous scan model so new exposure is seen before it becomes an incident
Windhoek
San Francisco
New York
Tokyo
London
Sydney
Cape Town
Dubai
Paris
São Paulo
Windhoek → London
SF → Tokyo
NYC → London
Global coverage · live threat surface